We build it compliant. Your lawyers sign it off.
Let's be clear from the first line: we are not lawyers and we do not give legal advice. What we do is build websites and apps where data protection is part of the design, not a patch added at the end.
The GDPR calls this data protection by design and by default (Article 25): collect only the data you need, keep it only as long as you need it, and protect it from the start. The European Data Protection Board explains what this means in practice in its guidelines on Article 25.
How we work with your legal team
- We look at what your site or app collects, where the data goes and how long it stays.
- We propose changes to policies, consent and data flows, and we build them.
- Your lawyers or your legal department review and validate them.
So far, every change to policies and flows we implemented for our current clients has been accepted by their legal departments.
What we build
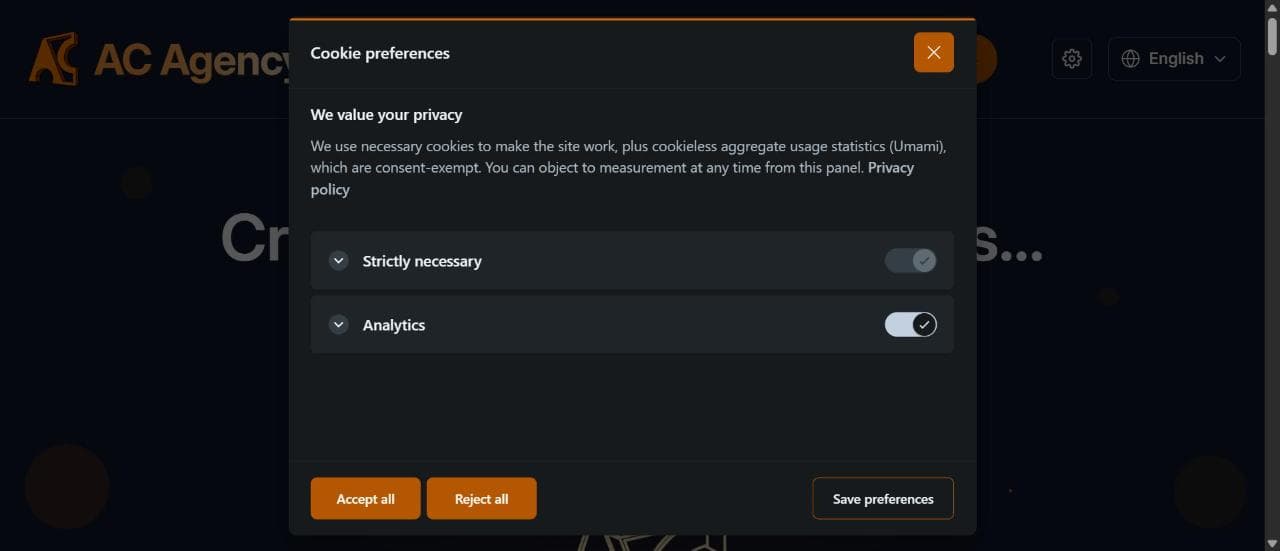
- consent and cookie management that respects the visitor's choice;
- analytics that measure visits without collecting more personal data than needed;
- forms and flows that ask only for what is necessary;
- ways to handle requests from people who want to see, correct or delete their data;
- updates to privacy and cookie policies, ready for your lawyers to review.
Our own site is the first test
This website uses no tracking cookies and no advertising pixels. Visitor statistics come from a cookie-free tool we host in the European Union, and the site itself is hosted in the EU. Everything is described in our privacy policy.
Planning a new site or app, or reviewing one you already have? Tell us what it collects today.
Talk to us about your projectAC Agency: we build it, your lawyers validate it.